Table of Contents
- Start With a Vulnerability Analysis, Not a Template
- OSHA Emergency Action Plan Requirements: What Inspectors Actually Check
- Risk Assessment Tools for Industrial Facilities: From HAZOP to Bowtie
- Industrial Emergency Response Templates: Building Yours From Scratch
- Emergency Preparedness Drill Frequency: How Often Is Enough?
- Cyber-Physical Security: The Gap Most Industrial Plans Miss
- Supply Chain Resilience and Post-Crisis Recovery for Industrial Operations
- Frequently Asked Questions
Last Updated: September 13, 2026
Start With a Vulnerability Analysis, Not a Template
Most industrial emergency preparedness failures start when a safety manager downloads a generic industrial emergency preparedness template, fills in the blanks, and files it. That document will not survive a real crisis or an OSHA inspection.
A vulnerability analysis is a structured assessment of what could go wrong at your facility, how likely each scenario is, and what the consequences would be. Unlike a template, it is built from your processes, chemicals, equipment, and people.
Start with three inputs:
- A walkthrough of every process area, including storage, loading, and maintenance
- Your OSHA 300 logs and near-miss reports from the past three years
- Interviews with the people who actually run the equipment
The output is a ranked list of credible scenarios. Everything downstream, from evacuation routes to drill frequency, flows from that list.
OSHA Emergency Action Plan Requirements: What Inspectors Actually Check
The answer is straightforward: OSHA’s emergency action plan standard, 29 CFR 1910.38, requires a written plan covering escape procedures, escape route assignments, procedures for employees who remain to operate critical operations, accounting for all employees after evacuation, rescue and medical duties, and the names of people to contact for further information. Inspectors check whether your plan exists, whether it is current, and whether your employees know it.
What most guides miss is the gap between having a document and having a plan. An inspector will ask a line worker where the nearest exit is and who the assembly point coordinator is. If the answer is a shrug, the written plan does not matter.
The Industrial Overlay Most Plans Miss
For facilities handling hazardous substances, 1910.38 is only the floor. Two additional standards reshape what your plan must contain:
- 29 CFR 1910.120(q), HAZWOPER emergency response. Any employee expected to respond to a release rather than evacuate must be trained to a defined response level (awareness, operations, technician, or specialist), and the plan must state which level applies to which role. The most common citation: a facility that trains everyone to awareness level but expects operations-level tasks during a spill.
- 29 CFR 1910.119(n), Process safety management emergency planning. PSM-covered facilities must have a written emergency action plan addressing small releases handled by employees and large releases requiring evacuation, reviewed with employees after each drill or incident.
If your facility handles highly hazardous chemicals, an inspector will check that the PSM plan and the 1910.38 plan are consistent. Conflicting assembly points or notification chains between the two documents is a common finding.
What Documentation Actually Holds Up
A citation usually comes from a missing record, not a missing intention. Records that survive scrutiny:
- A plan review date within the last twelve months, with a named reviewer
- Training records tied to specific employees and specific plan elements, not a sign-in sheet
- Drill reports with observed deficiencies and corrective actions, each with an owner and a close date
- A clear chain of command for incident command, including who assumes command on off-shifts
- Annual review of the plan with each covered employee, documented
A common mistake is treating the written plan as the deliverable. If your training records cannot show that every employee covered by the plan has actually been trained on it, the plan itself becomes the citation. The same logic applies to contractor personnel working inside your fence line, if they are on site when an alarm sounds, they are covered by your accountability procedures, and the inspector will ask how you account for them.
The Off-Shift and Contractor Blind Spot
Inspectors frequently probe scenarios the plan was not written for. Two questions come up repeatedly:
- Who is the incident commander on the night shift? If your plan names a day-shift role by title and that person is not on site, the plan is silent on the thinnest-staffed shift.
- How do you account for contractors, delivery drivers, and visitors? Sign-in sheets fail when the gatehouse is evacuated; badge-in systems fail when the network is down. Plans that hold up use a physical backup, a printed roster, a roll-call at the assembly point, or a buddy system for short-duration visitors.
The Practical Test
Before your next inspection cycle, pull three random line employees and ask them to name the assembly point, the person who accounts for their area, and the secondary route if the primary is blocked. If any cannot answer, the plan is not ready, regardless of what the binder says.
Risk Assessment Tools for Industrial Facilities: From HAZOP to Bowtie
Risk assessment tools for industrial facilities range from qualitative checklists to formalized methods like HAZOP, LOPA, and bowtie analysis. The right choice depends on process complexity and consequence of failure, not on which method sounds most rigorous.
HAZOP (Hazard and Operability Study) is a team-based method that examines each process node for deviations from design intent. It suits chemical and refining operations where piping and instrumentation diagrams drive the analysis.
Bowtie analysis maps threats on one side, consequences on the other, and the barriers standing between them. It is the clearest way to show leadership where your controls are thin.
LOPA (Layer of Protection Analysis) quantifies how many independent protection layers stand between a scenario and a release. Use it when you need to justify a safety instrumented system.
| Method | Best For | Team Size | Typical Output |
|---|---|---|---|
| HAZOP | Complex process units | 5-7 people | Deviation list with safeguards |
| Bowtie | Communicating risk to leadership | 3-5 people | Barrier map with gaps flagged |
| LOPA | Justifying safety instrumented systems | 3-4 people | Required risk reduction target |
| Checklist | Routine, low-complexity tasks | 1-2 people | Pass/fail compliance record |
The mistake is running a HAZOP on a process nobody has diagrammed in a decade. Fix the drawings first.
Industrial Emergency Response Templates: Building Yours From Scratch
No template fits an industrial facility, because hazards, layout, and staffing differ at every site. What you can reuse is the skeleton.
Build your plan around these sections, in this order:
- Scope and authority. Name who owns the plan and who can activate it.
- Hazard inventory. List every material and process with a credible release or fire scenario.
- Notification and communication. Define who calls whom, and how.
- Evacuation and shelter-in-place. Include primary and secondary routes, plus assembly points.
- Accountability. Specify how you confirm every person is out or sheltered.
- Incident command. Assign roles: incident commander, safety officer, liaison.
- Recovery and reentry. State who authorizes reentry and under what conditions.
- Training and drill schedule. Tie each role to a required competency.
The FEMA Emergency Management Institute publishes free course material on incident command that maps cleanly onto industrial settings.
Build the accountability section before the evacuation section. Knowing who is on site at any given moment, contractors included, is harder than drawing exit routes, and it is where most plans collapse in a real evacuation.
Emergency Preparedness Drill Frequency: How Often Is Enough?
OSHA does not set a universal drill frequency for most facilities, but every employee covered by your plan should practice it at least annually, with higher-risk roles drilling more often. Facilities handling highly hazardous chemicals under PSM generally drill more frequently as part of their compliance obligations.
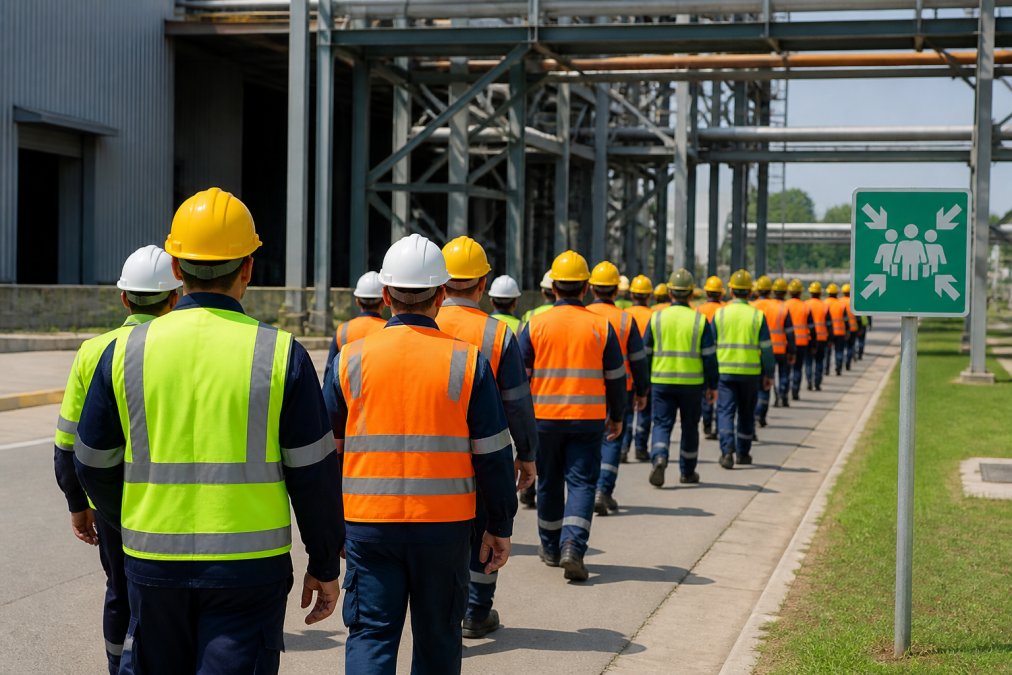
Frequency alone is not the measure. A drill that runs smoothly every time is probably not testing anything. Vary the scenario: block a primary exit, simulate a communication failure, run a night shift drill with reduced staffing.
What to track after every drill:
- Time from alarm to full accountability
- Number of employees who took an incorrect route
- Equipment or communication failures observed
- Corrective actions assigned and closed
Review the drill report as seriously as an incident report. The deficiencies you find in a drill are the ones you will not find during a real event.
Cyber-Physical Security: The Gap Most Industrial Plans Miss
Most industrial emergency plans treat cybersecurity and physical safety as separate worlds. They are not. A ransomware attack that locks your control system, or a compromised sensor feeding false readings to an operator, is an emergency with the same consequences as a valve failure.
Cyber-physical security integration means your emergency plan accounts for scenarios where the threat arrives through the network. That includes:
- Loss of SCADA or distributed control system visibility
- Manipulated sensor data driving wrong operator decisions
- Ransomware that disables your emergency notification system
- Physical access control systems rendered inoperable
The federal government’s lead agency for infrastructure security publishes sector-specific guidance through CISA’s industrial control systems resources. Fold those scenarios into your vulnerability analysis rather than maintaining a separate IT document nobody on the floor has read.
If your emergency notification system depends on the same network as your control system, you have a single point of failure. Test your notification path with the network down.
Supply Chain Resilience and Post-Crisis Recovery for Industrial Operations
A facility can survive the incident and still fail in the months that follow. The recovery phase is where most industrial plans are thinnest, and where two commonly missed gaps, supply chain resilience and a structured post-incident audit loop, determine whether the organization actually recovers or just restocks.
Supply Chain Resilience: Map Before You Need It
Supply chain resilience during an industrial crisis means knowing which single-source suppliers would halt your recovery, and having a qualified alternate identified before you need one. The failure mode is discovering three weeks later that the only qualified vendor for a critical replacement part is the one whose facility burned in the same regional event.
Map your critical inputs and ask four questions for each:
- If this supplier went offline for thirty days, what stops?
- Is there a qualified alternate already approved, or only a name on a list?
- How long would requalification take, and who owns that process?
- Does the alternate sit in the same geographic or logistical corridor as the primary?
The fourth question is the one most plans skip. Two suppliers in the same flood plain, the same hurricane track, or the same rail corridor are one supplier for resilience purposes. Geographic diversity is a resilience property, not a procurement preference.
For regulated industries, requalification is the real constraint. A replacement supplier for a food, pharmaceutical, or aerospace input may need audits, sample approvals, and customer notification before a single part ships. Build that timeline into your recovery assumptions rather than discovering it during an event.
The Human Dimension of Recovery
Post-crisis recovery also has a human dimension most plans ignore. Employees who witnessed a serious injury or fatality carry psychological load that affects their ability to return to the same equipment. Plan for it: employee assistance resources, phased return to the affected area, and supervisors trained to recognize when someone is not ready.
The practical mechanism is a phased reentry: bring back a small group for a walkthrough, then a partial shift, then full operations, pairing each phase with a check-in. Supervisors are not clinicians, but they can be trained to notice when someone needs support rather than a schedule.
The Post-Incident Audit Loop
After the immediate response closes, run a post-incident audit: compare what the plan said would happen against what actually happened, and revise the plan accordingly. That feedback loop separates an organization that learns from one that simply restocks and moves on.
A workable audit structure has four parts:
- Timeline reconstruction. Build an hour-by-hour account from alarm to all-clear, using logs, radio traffic, and interviews. Memory is unreliable; records are not.
- Plan-versus-actual comparison. For each plan element, notification, evacuation, accountability, incident command, note where execution matched the plan and where it diverged.
- Root cause of divergence. A divergence is not automatically a failure. Sometimes the plan was wrong; sometimes the plan was right and the training was thin; sometimes the plan was right and the equipment failed. Each has a different fix.
- Corrective actions with owners and dates. An audit without assigned actions is a report, not a loop.
The audit is the only part of the preparedness cycle that improves the plan using real data. Drills test assumptions; an actual incident reveals which assumptions were wrong. Treat the post-incident audit with the same formality as the incident investigation itself, and close the loop before the next drill cycle begins.
Closing the Loop
The organizations that recover well from industrial crises are not the ones with the longest plans. They mapped their supply chain before the event, planned for the human cost of the response, and ran a disciplined audit afterward. Those three practices turn a single incident into a stronger plan rather than a repeated one.
Frequently Asked Questions
What are the essential components of an industrial emergency action plan?
An industrial emergency action plan must include evacuation routes and procedures, shelter-in-place protocols, a method for accounting for all personnel after evacuation, rescue and medical duties, names of emergency coordinators, and communication procedures for reporting emergencies. OSHA requires these elements under 29 CFR 1910.38. For high-stakes industrial settings, add hazard identification for specific chemicals or processes on site, incident command structure, and coordination with local fire and hazmat responders.
How often should a company update its emergency preparedness plan?
Review your industrial emergency preparedness plan at least annually, and after any drill, near-miss, or actual incident. OSHA requires updates when facility layout, processes, or personnel change. High-stakes industrial operations should review quarterly if they handle hazardous materials or run continuous processes. Assign a specific emergency coordinator to track changes and document each revision so inspectors can see a clear maintenance history.
What are the OSHA requirements for industrial emergency action plans?
OSHA 29 CFR 1910.38 requires a written emergency action plan covering escape procedures, headcount methods, rescue duties, reporting procedures, and emergency coordinator names. Employers must review the plan with each employee when it is created, when responsibilities change, and when the plan itself changes. For facilities with 10 or fewer employees, the plan may be communicated orally. Industrial sites handling hazardous substances also fall under 29 CFR 1910.120, which adds emergency response training and hazmat-specific requirements.
How do you conduct an effective risk assessment for industrial facilities?
Start with a vulnerability analysis that maps every hazard: chemical, mechanical, electrical, thermal, and cyber-physical. Use structured tools like HAZOP for process hazards, bowtie analysis for high-consequence events, and job hazard analysis for routine tasks. Score each risk by likelihood and severity, then prioritize mitigation strategies. Involve floor-level workers, not just management, because they see near-misses that never reach incident reports. Document everything and revisit the assessment after any process change.
 Michael Karl McNeil

Leave a comment